HWP document malware inspection and removal
A desktop tool for inspecting and removing suspicious elements in HWP document streams. I implemented binary parsing and file-signature checks and connected an external scanning service.
Screens
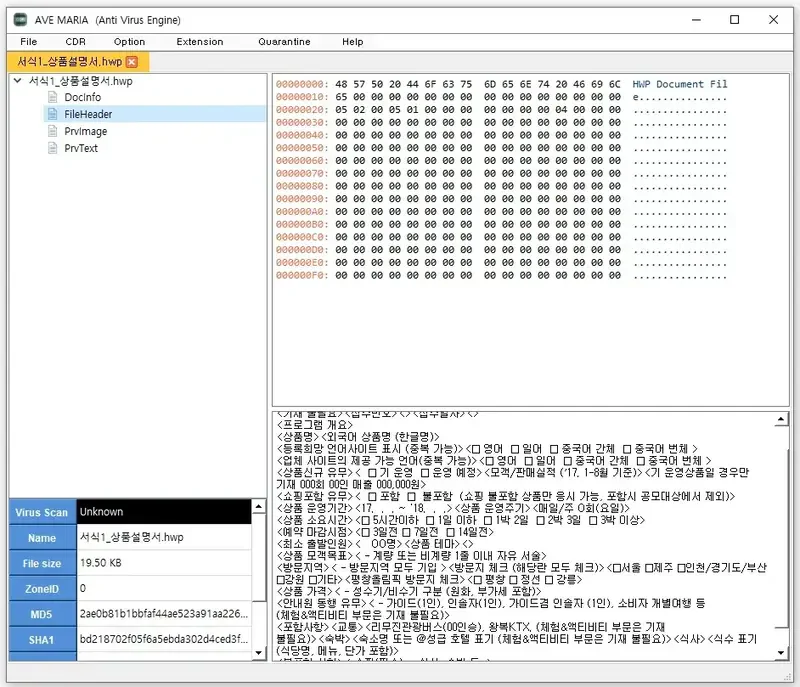
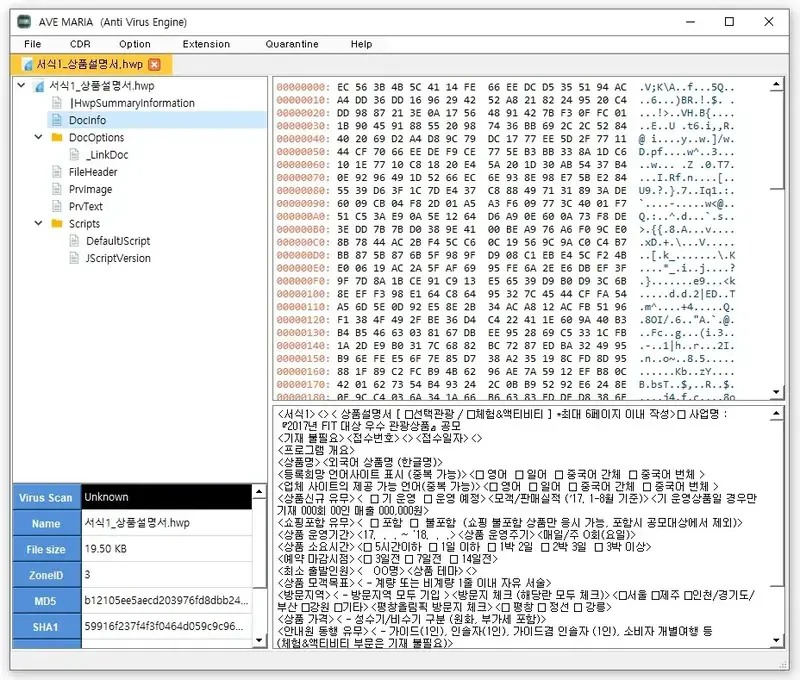
Inspecting the internal file structure
I parsed OLE2 binaries to inspect and process individual streams. Hex signatures identify the actual format behind a disguised extension, and I modified an existing library where additional behavior was needed.
Desktop interface and external scanning
I built the interface with Python and PyQt5 and integrated the VirusTotal API, combining internal document analysis with an external inspection service.